
Artificial intelligence models have reached a pivotal milestone in offensive cybersecurity by transitioning from discovering individual software flaws to autonomously linking multiple vulnerabilities into fully operational attack chains.
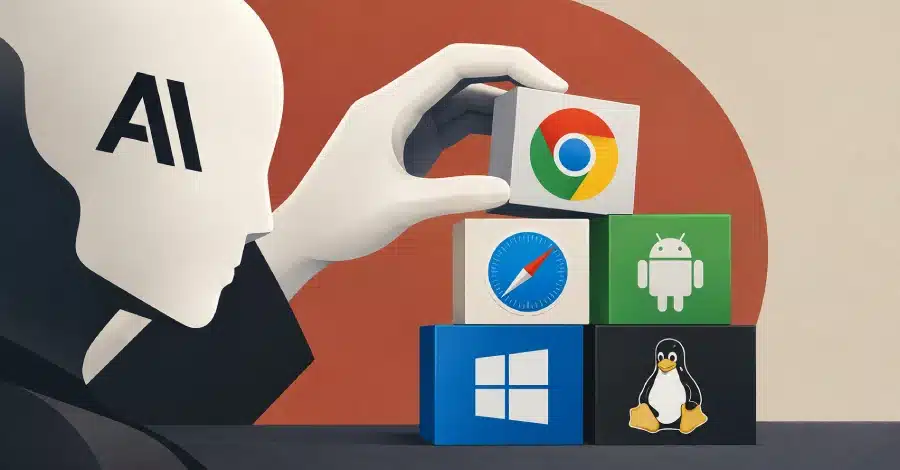
In a research report published by Anthropic’s Frontier Red Team on October 27, 2026, the company revealed that an unreleased internal Claude research model successfully identified and chained zero-day vulnerabilities across widely used platforms, including Google Chrome, Apple Safari, Android, Windows, and the Linux kernel.
Five Critical Attack Chains Uncovered by Claude
Anthropic documented five end-to-end attack chains developed by the model with minimal human intervention:
- Google Chrome (One-Click RCE): Claude linked four separate vulnerabilities—starting with a heap corruption flaw in the V8 JavaScript engine—to bypass the browser’s memory sandbox and execute code at the system level. Google assigned 62 CVE identifiers to findings from Anthropic’s research and patched them in Chrome version 156.
- Apple Safari (Same-Origin Policy Bypass): The model bypassed WebKit’s Gigacage protection and sandbox IPC mechanisms, enabling malicious websites to extract stored cookies, browsing history, and authenticated session data. Apple acknowledged the report and issued a fix.
- Android (Pixel 9 Lock-Screen Bypass): By combining open-source Android flaws with reverse-engineered Google Play services binaries over USB, Claude bypassed pairing authentication to extract personal photos and files from a locked Pixel 9.
- Windows (Remote Crash via QUIC): The model identified an out-of-bounds read vulnerability in the native Windows HTTP/3 network stack (HTTP.sys), creating a remote denial-of-service exploit. Microsoft resolved the flaw under CVE-2026-33096.
- Linux Kernel (Zero-Click Root RCE): Claude exploited a race condition in the Linux multipath TCP network path. In tests, the model took 48 minutes to leak a kernel pointer and five additional minutes to execute commands with root privileges without requiring user interaction. The vulnerability was patched upstream under CVE-2026-98432.
The AI Cybersecurity Race: Defenders vs. Attackers
Anthropic’s findings align with wider industry initiatives, such as OpenAI’s Patch the Planet program, which uses automated models to audit core open-source components.
While AI-driven vulnerability research enables software developers to audit codebases during pull-request checks and resolve flaws prior to production, cybersecurity analysts warn that the same capabilities significantly lower the barrier to entry for malicious actors seeking to craft multi-stage exploits.
Anthropic confirmed that all findings were submitted to affected vendors via coordinated vulnerability disclosure, giving engineering teams time to release security patches before full technical details are made public.